A transformation, driven by cloudification and automation, of all Aadhaar enrollment, data storage and access processes is a key need today
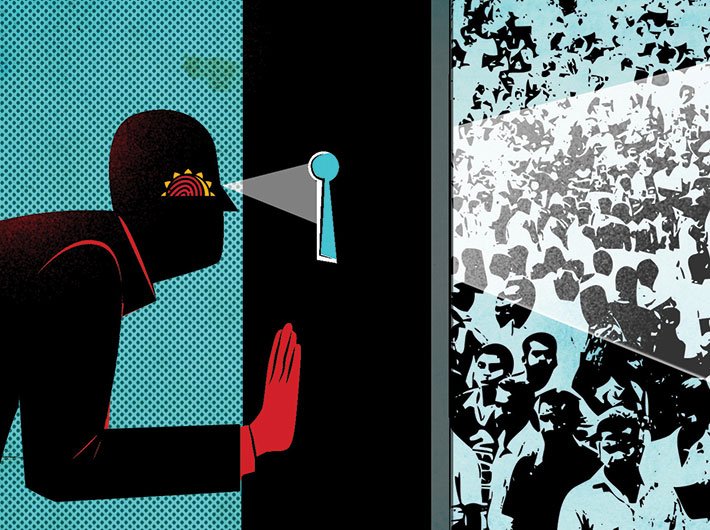
In this digital and social media age, the din about privacy is seemingly a big paradox. How come a generation that is so comfortable sharing the minutest details about their whereabouts, families and friends, and so candid about voicing their political, social and ideological views on open platforms like Facebook and Twitter, be bothered about a potential risk to privacy in a secure network like Aadhaar?
As attorney general Mukul Rohatgi has argued before a supreme court bench, “privacy” has been a vague concept and an earlier judgment had held it was not a “guaranteed right” under the constitution. As such, citing privacy concerns can indeed not be a basis to petition against the implementation of the Aadhaar scheme.
However, there also lies a counter argument: how come a vague concept be used as a basis to implement a scheme that potentially infringes upon privacy of citizens?
The debate around privacy, due to the vagueness surrounding it, can be a double-edged sword, which could be used to further either sets of arguments.
Why not do away with the vagueness?
Logically, defining the boundaries by which a government agency must adhere to when using the Aadhaar linked information of individuals should help settle the debate. For example, while it is certainly important to mandate use of Aadhaar numbers (at most in a phased manner), it is equally important that not every recorded activity be discretely passed on to various departments.
As a broad analogy, think of the call data records (CDRs) in the telecom billing systems. CDR information is shared with the government law enforcement agencies only in instances when a person is wanted or suspected in an illegal or anti-national activity, as an example. All Aadhaar-linked data should also be provisioned to lie dormant as long as the activities of individuals follow a normal pattern. Only when an aberration or breach is officially reported by a concerned agency should the information be shared.
In fact, by making use of sophisticated analytics, it would be very much possible to even define the aberrations in Aadhaar-linked activities of individuals that should raise a trigger, which in turn could draw the attention of a concerned official for any follow-up action. The analytics engine could continually be refined by being fed with new definitions of aberrations and trigger points as and when those are discovered.
Transparency is the key
The processes defining the trigger points should be well documented and made available for audit, say, to an independent panel of experts comprising a mix of technology, legal and constitutional experts, among other relevant members, if any.
Of course, individuals with criminal or terrorist records could be included in a threat list at the very outset, so as to ensure that their movements are duly captured and monitored in a more discrete manner. At the same time, the list may also be shared with the panel to ensure that no innocent citizen, whether by design or by error, gets labelled as a criminal in the records.
Also, it is important to ensure that certain types of data, like the health records, should constitute a privacy core with very stringent access parameters, and should be shared with other agencies only in the rarest of rare circumstances.
Implementation challenges
The biggest challenge, perhaps, would lie in the fact that different government departments and processes are at varying stages of digitisation, something that would make a uniform implementation of Aadhaar analytics difficult to begin with.
Moreover, defining the aberrations, triggers and exceptions in a vast set of Aadhaar-linked data can be a complex and time consuming process, and as such could be potentially frustrating for the implementing agencies.
Moreover, unlike PAN cards, which due to a linkage with income taxes tend to cover only a part of the population, Aadhaar cards are aimed at the entire population universe and hence also pose greater challenges of scale. Also, the bottom-of-pyramid socioeconomic segments would need to be incentivised to become part of the Aadhaar fold. This, in turn, poses its own set of challenges.
These, and other, challenges are reflected in the fact that the target of achieving 100 crore Aadhaar enrolments by June 2015 has turned out to be elusive.
App-ification of Aadhaar registration
It may be a good idea to leverage an already large — and growing — base of smartphone wielding mobile service subscribers in the country. One conceptually simple way would be to make it possible for people to register using an Aadhaar app. Further, if these mobile subscribers are also provisioned to do Aadhaar registrations for their family members using the same app, maybe subject to a physical verification to be carried out later, the whole process may be greatly speeded up. (Of course, other existing Aadhaar registration systems may continue to work in parallel).
Since mobile subscribers have already been verified through know your customer (KYC) processes in the past, the mobile numbers could actually serve as the first points of authentication. Also, it is not hard to conceive telcos as potential partners in this whole Aadhaar registration process. Their newfound capabilities in video-based solutions could be particularly helpful.
Leverage cloud to better privacy?
Counterintuitive though it may sound, cloudification of the registration process as well as access to all Aadhaar data could actually help address a large body of privacy-related concerns.
As of now, various private-sector implementation agencies have been contracted to speed up the Aadhaar registration process, which makes the data being captured vulnerable to unauthorised access. Moreover, there is a lot of manual intervention in the data capturing process and the data is also often stored locally, which further increases the risks of privacy breaches. For example, data such as fingerprint and iris scan are highly sensitive and any misuse of that could pose serious threats to the concerned individuals.
By digitising the entire enrolment process and making all data storage and access cloud based, it is quite possible to insulate personal data in a way that it is not subject to any manual intervention, even if the existing agencies and enrolment centres continue to serve as facilitators.
However, a valid concern remains that all citizen data that has hitherto been captured lies exposed. While destroying all localised records could mitigate the risks to a large extent, other safeguards would also need to be taken. This can be taken up as a separate activity by the concerned authorities.